
The frameworks you are measured on, in one place
Choose the right size for each business unit, from a short essentials set to the full framework. Every question has help text, risk and action text, and written steps to close the gap.
CIS Controls v8.1
The practical, prioritised set of safeguards from the Center for Internet Security. A good place to start for most organisations.
ISO/IEC 27001:2022
The management system clauses 4 to 10 and all 93 Annex A controls, with a Statement of Applicability report.
NIST CSF 2.0
One question per subcategory of the NIST Cybersecurity Framework 2.0, including the new Govern function.
POPIA
The Protection of Personal Information Act: the Information Officer, the eight conditions, breaches, data subject requests and operators, plus baseline security.
Joint Standard 2 of 2024
The FSCA and Prudential Authority cybersecurity and cyber resilience requirements for financial institutions, with paragraph references.
PCI DSS v4.0.1
The payment card industry standard for anyone who stores, processes or transmits card data, across all 12 requirements.
Cyber Essentials
The five technical controls of the UK Cyber Essentials scheme (v3.3): firewalls, secure configuration, updates, user access and malware protection. A quick baseline for smaller organisations.
Supplier security questionnaire
Based on NIST SP 800-161. Your service providers answer it themselves, sized to how critical they are to you.
See how your work in one framework reaches the others
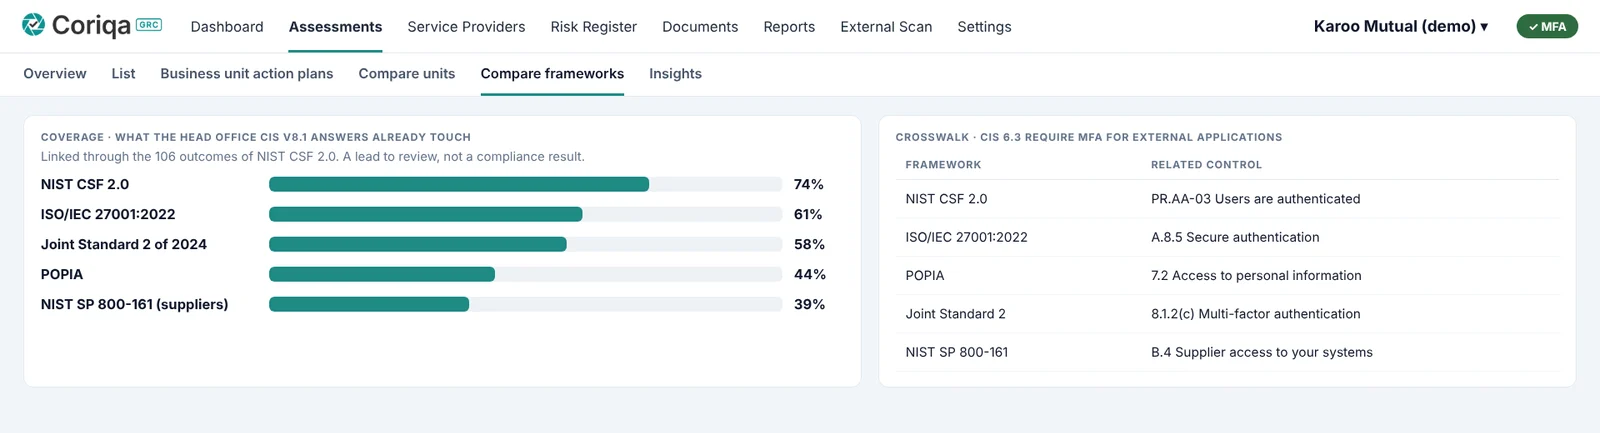
All eight frameworks are mapped through the 106 outcomes of NIST CSF 2.0. After a CIS assessment, you see how much of ISO 27001, Joint Standard 2 or POPIA your Yes and Partial answers already cover, the related control in every other framework, and where your answers disagree.
Start the next framework with those answers already filled in. Each one is marked to confirm, so nothing counts until someone has checked it against the new framework's wording.
Only answers that show a control is in place count. A "No" is flagged as a likely gap.
A simple way to choose
| If you are | Start with | Add later |
|---|---|---|
| A small or medium business without a security team | NIST CSF 2.0 Essentials or CIS IG1 | POPIA Essentials |
| Any organisation handling personal information | POPIA | CIS IG1 for the technical controls |
| An insurer, bank or other financial institution | Joint Standard 2 of 2024 | POPIA and ISO 27001 |
| Working towards ISO 27001 certification | ISO/IEC 27001:2022 | The document library and the Statement of Applicability |
| Taking card payments | PCI DSS v4.0.1 Essentials | PCI DSS Full and CIS IG1 |
| A group with many business units | CIS Controls v8.1 or NIST CSF 2.0 per unit | Supplier questionnaires for your service providers |
Not sure where to start?
We will help you pick the framework and size for each business unit.