
Run a vCISO service for every client, without hiring more CISOs.
Coriqa GRC is the cyber assessment, risk and compliance platform for South African consultants, vCISOs and MSPs. Assess a client, hand over a board pack and a remediation plan, and keep them on a recurring service.
Make security a service that grows
The four things that hold back a security practice, and how Coriqa GRC takes them away.
Anyone trained can run it
Every question explains what it asks, what each answer means and which evidence to keep, so a junior consultant delivers a consistent result.
Reports in a click
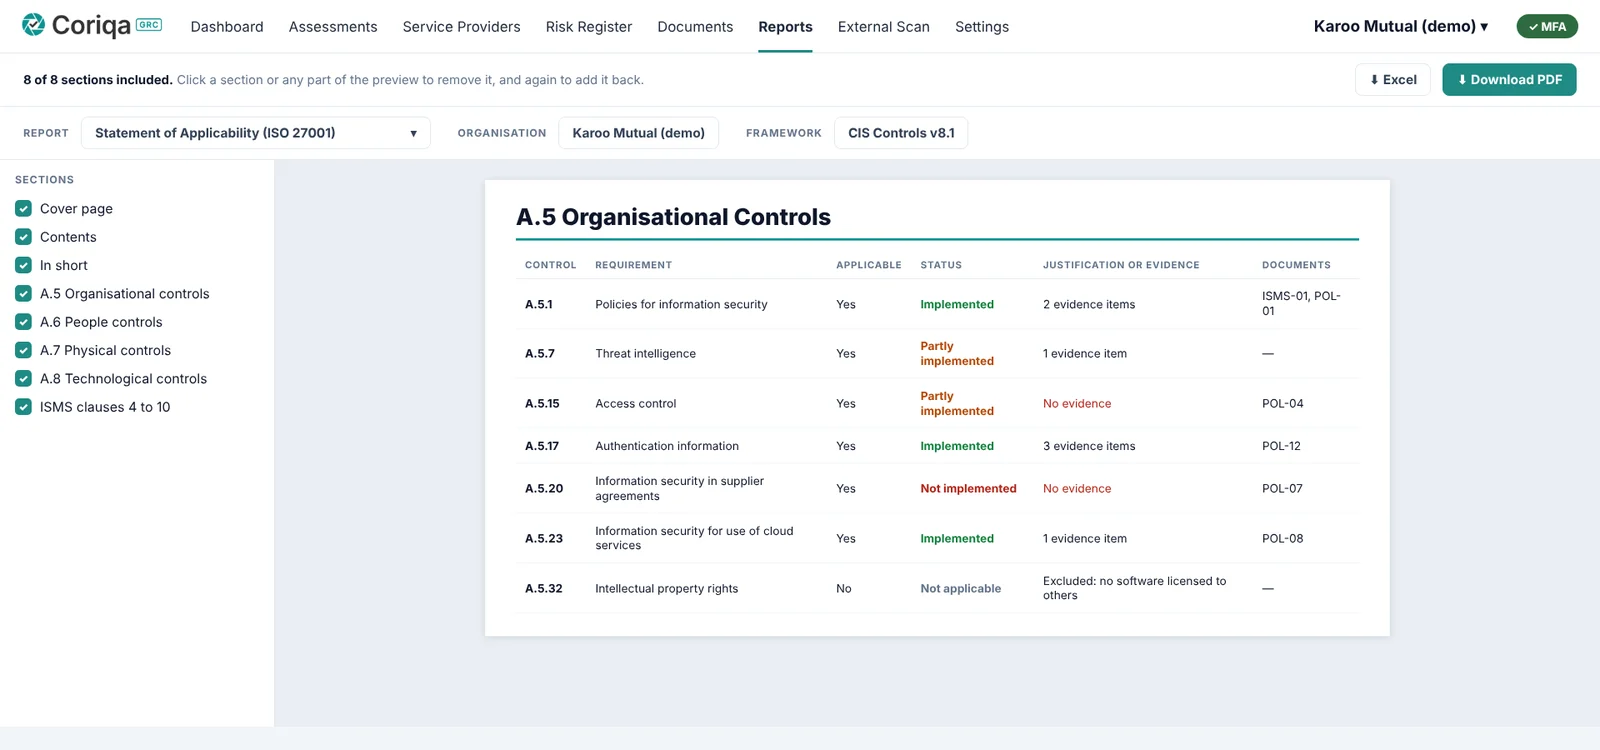
The board pack, assessment report and Statement of Applicability build themselves from the answers, with your logo on them.
Built for recurring work
Start with a once-off assessment, then keep the client on an ongoing service with repeat assessments and a live risk register.
A plan to work from
Every completed assessment ends in a remediation plan: what to fix, in which order, and the effort and impact of each step. Add the budget and proposal add-on to cost it with your own services and products.
See Coriqa GRC in two minutes
Client setup, an assessment, compare frameworks, the risk register, what-if, guidance, evidence and the board pack, using demo data.
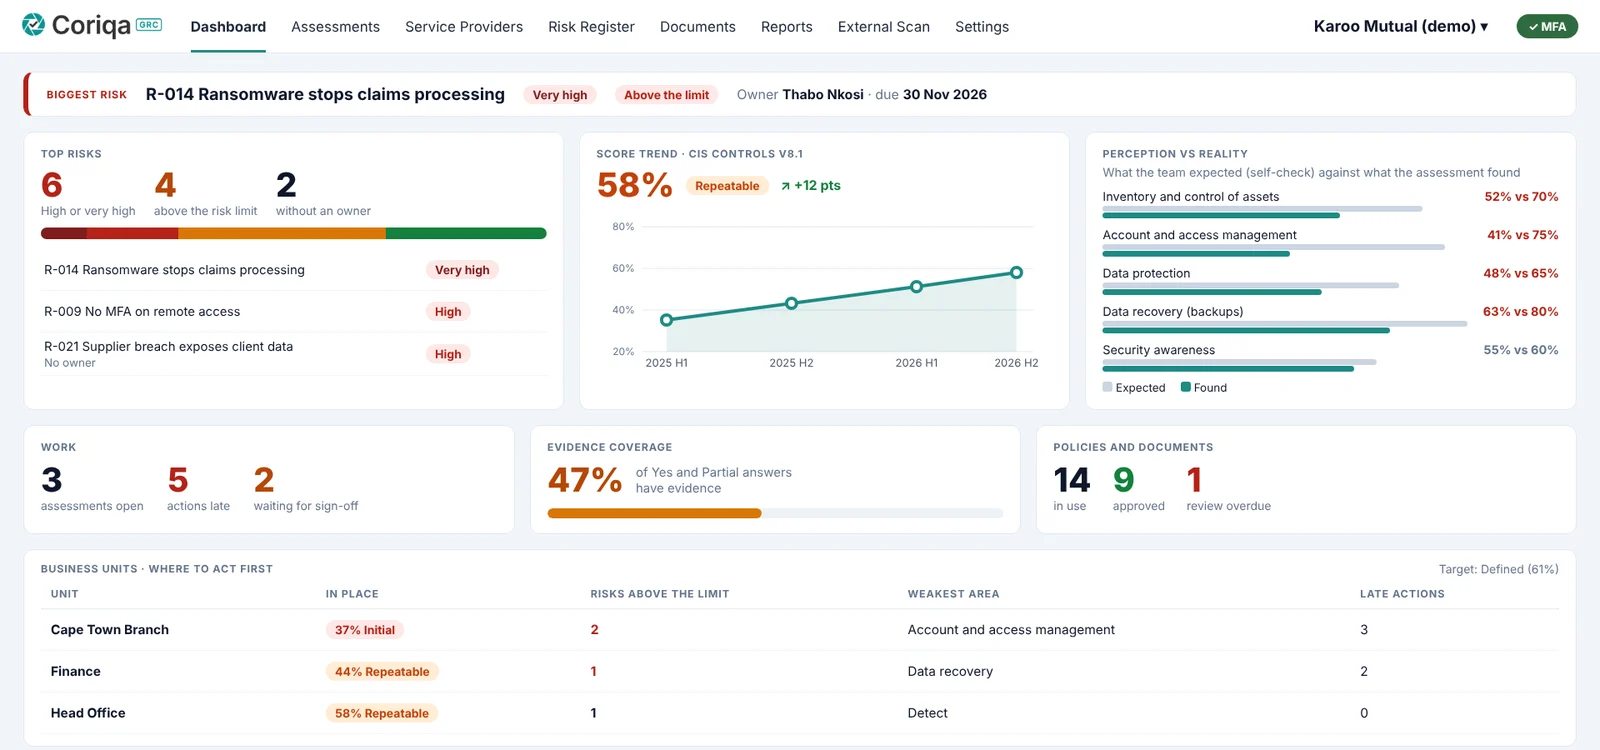
Every board asks the same three things
Measured per business unit against a recognised framework, and compared with what your team expected.
A risk register in plain words, with a risk limit, an owner and a due date for every risk.
Evidence on every answer, approved policies attached automatically, and reports built from the same data.
From finding a gap, to fixing it, to proving it
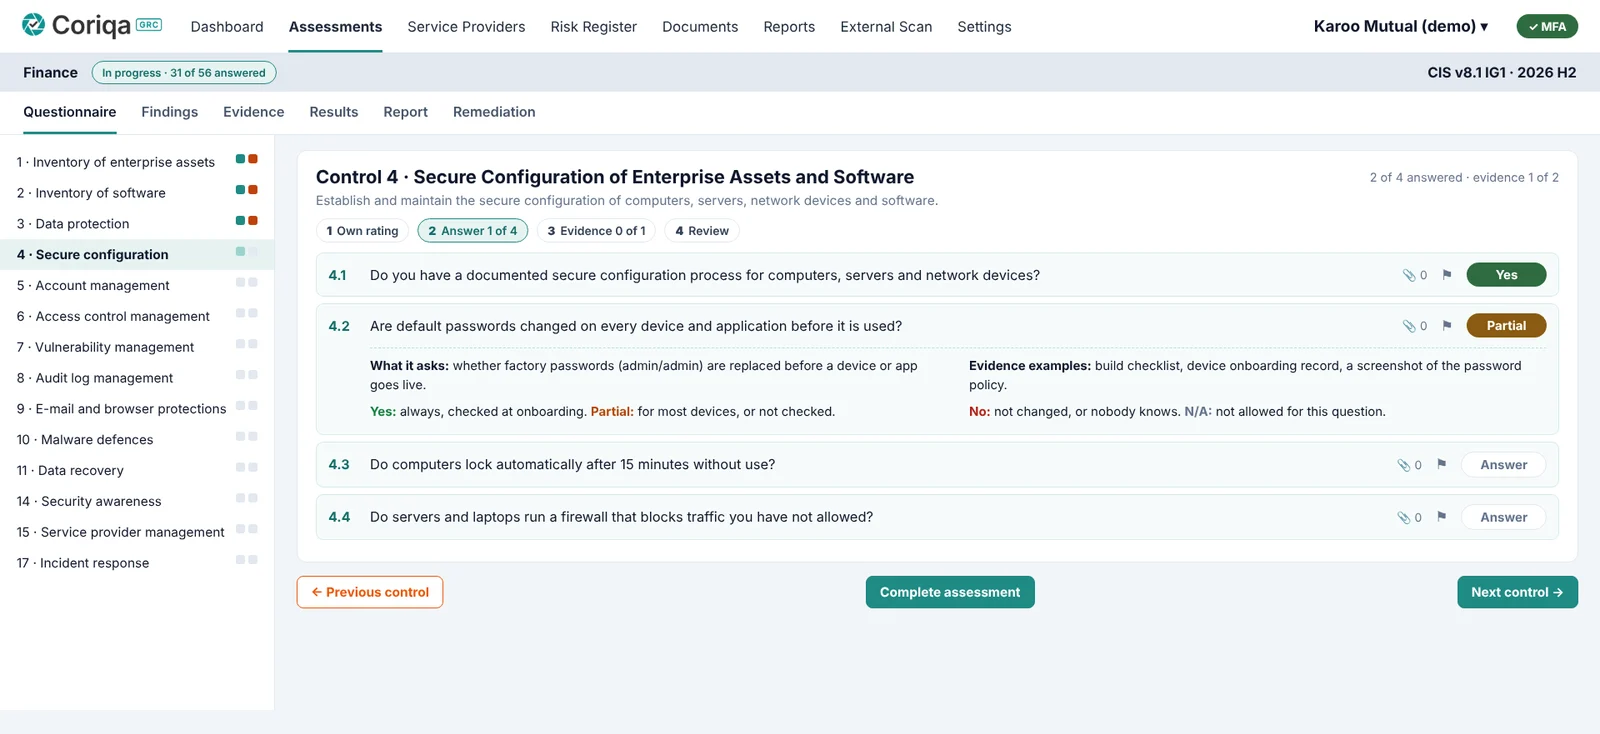
Your client's people answer the questions, guided one by one. You spend your time on advice, not spreadsheets.
Guided, one control at a time
Each question says what it asks, what Yes, Partial, No and N/A mean and which evidence to keep. N/A is only offered where a question can genuinely not apply.
- Flag "not sure" for the consultant instead of guessing
- Notes and files as evidence on the question
- Completing lists every Yes and Partial answer without evidence, and records it
- One assessment per business unit, with an action plan that carries forward
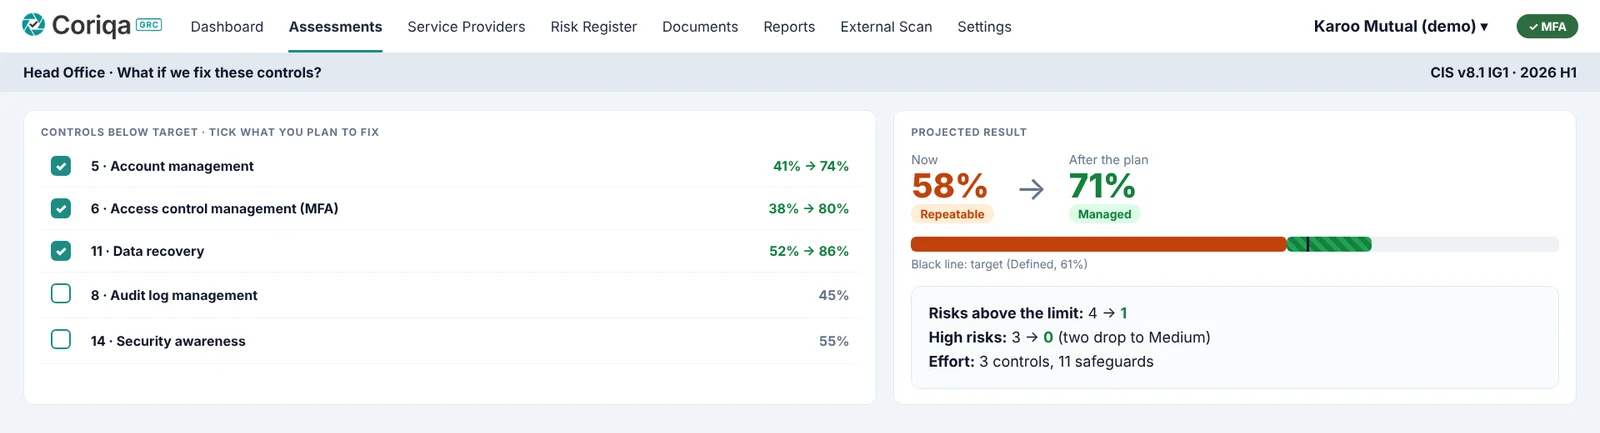
Know what to fix first, and what it will change
Maturity per function against the target you set, a risk matrix with your risk limit, and a what-if planner: tick the controls you plan to fix and see the score, the maturity level and your risks move.
- Likelihood, impact and effort for every control
- Business unit criticality taken into account
- Compare units and track the score over time
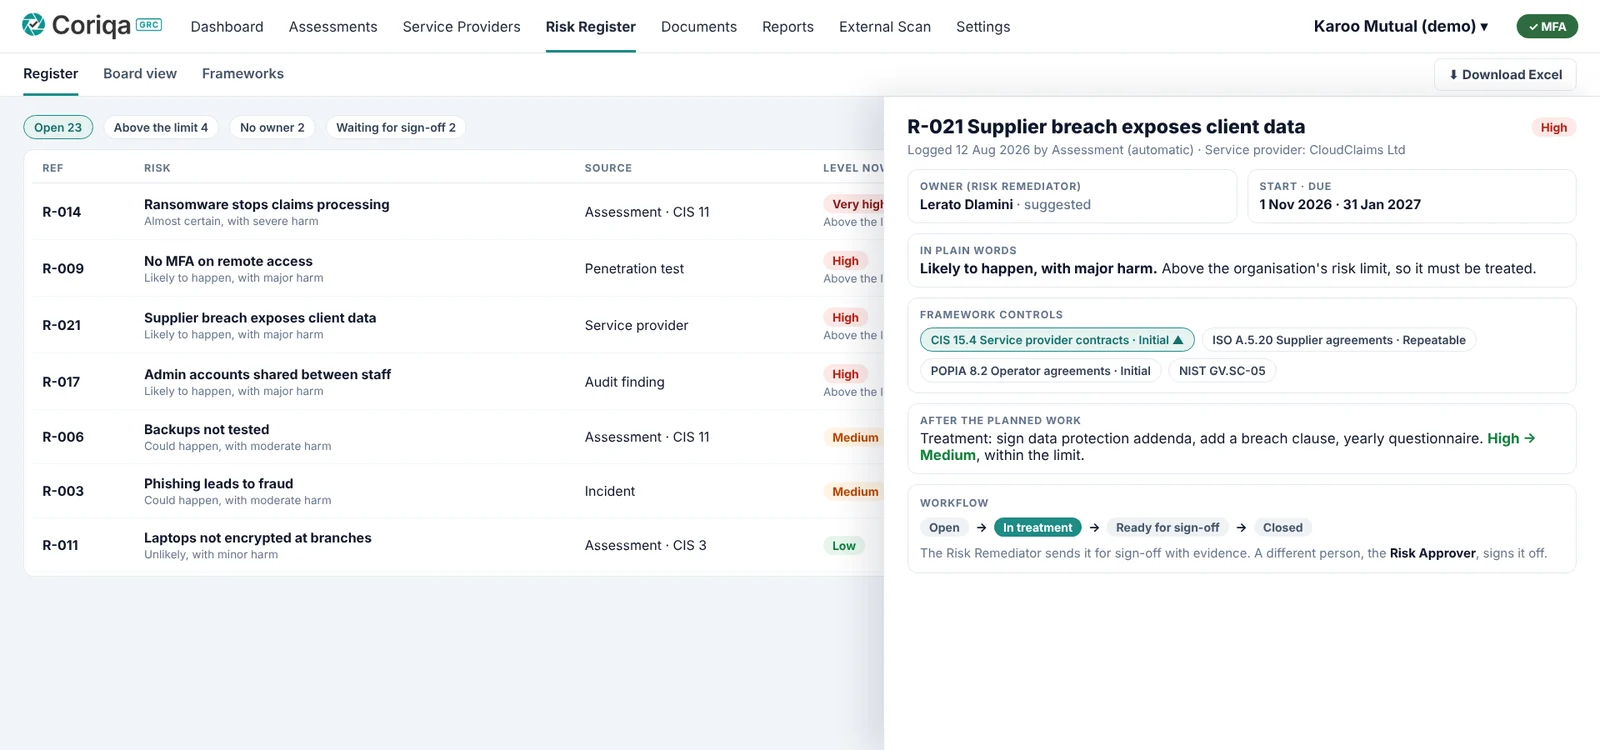
One register, in words the board understands
Risks are created from assessment gaps automatically and close themselves when a later assessment shows the control is fixed. Add your own from audits, incidents, penetration tests and suppliers.
- Method aligned with NIST SP 800-30, NIST IR 8286 and CIS RAM
- Open, in treatment, ready for sign-off, closed, with a full history
- Risk Remediator and Risk Approver roles keep duties separate
- Linked controls in every framework you use, and an Excel export
Written steps for every action
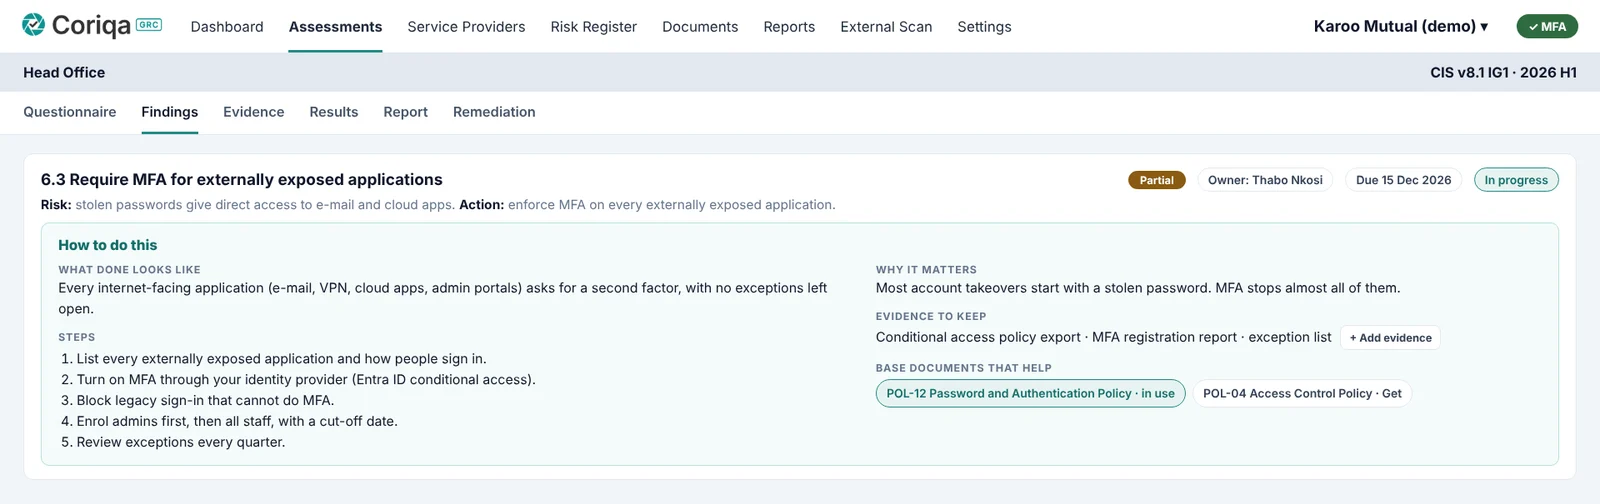
Under each action in the plan: what done looks like, three to five concrete steps, why it matters, the evidence to keep and the base documents that help.
- 533 questions across CIS, ISO 27001, NIST CSF 2.0, POPIA and Joint Standard 2
- Owner, due date and status per action
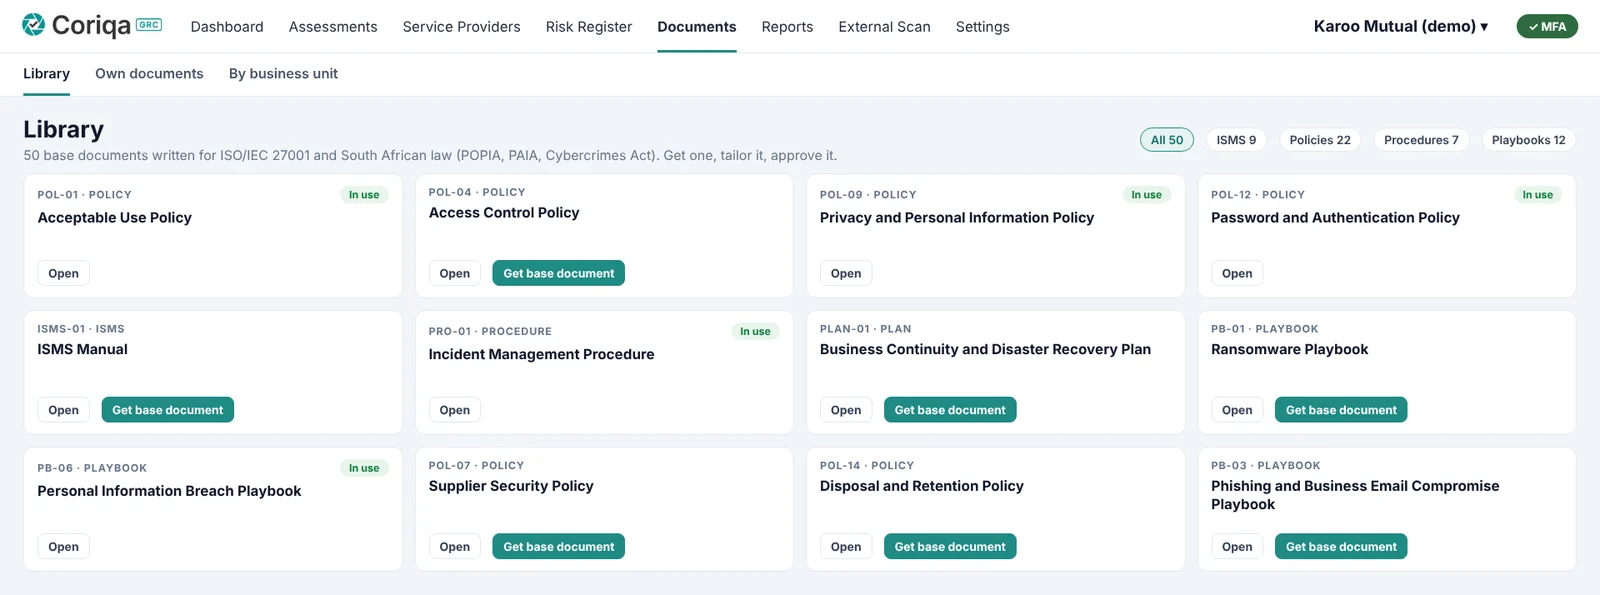
50 base documents, ready to tailor
An ISMS manual, Annex A policies, procedures, a business continuity and disaster recovery plan, and 12 incident playbooks, written for ISO 27001 and South African law (POPIA, PAIA and the Cybercrimes Act).
- Owner, status, versions, approval and review dates
- See which documents each business unit's framework asks for
- Base documents to tailor, not legal advice
Approve once, prove everywhere
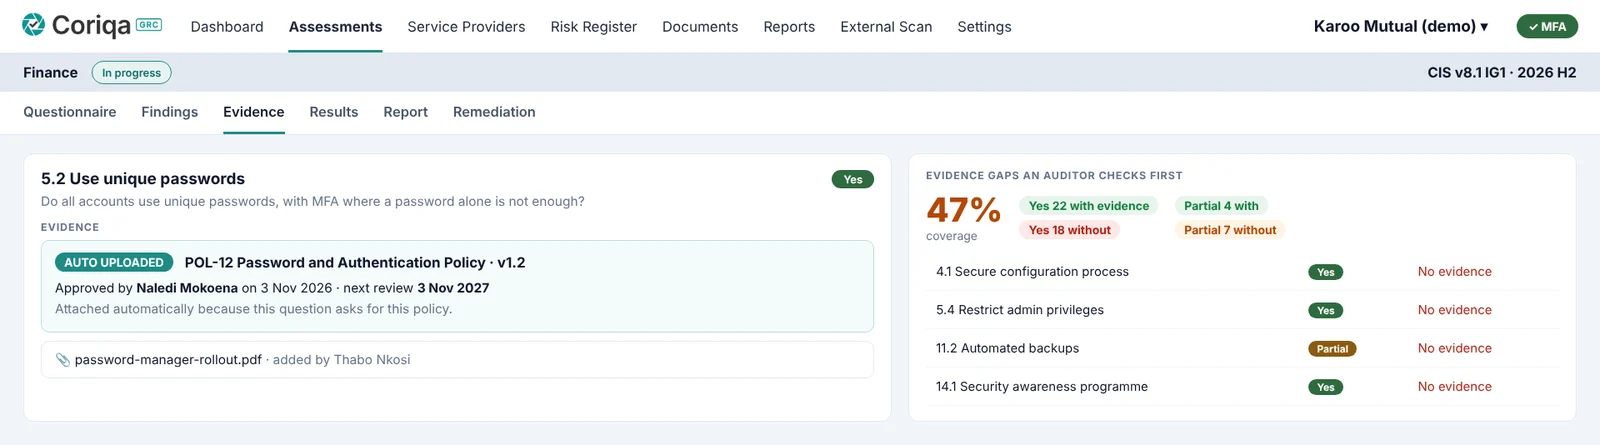
When a policy is approved with a review date, it is attached as evidence to every open assessment question that asks for it, marked with who approved it and when it is due for review.
- Evidence coverage per assessment and unit
- The self-declared answers an auditor checks first
- Answer once and reuse the answers and evidence in other frameworks
- Files encrypted and compressed, kept with the answer they prove
Your suppliers are part of your risk
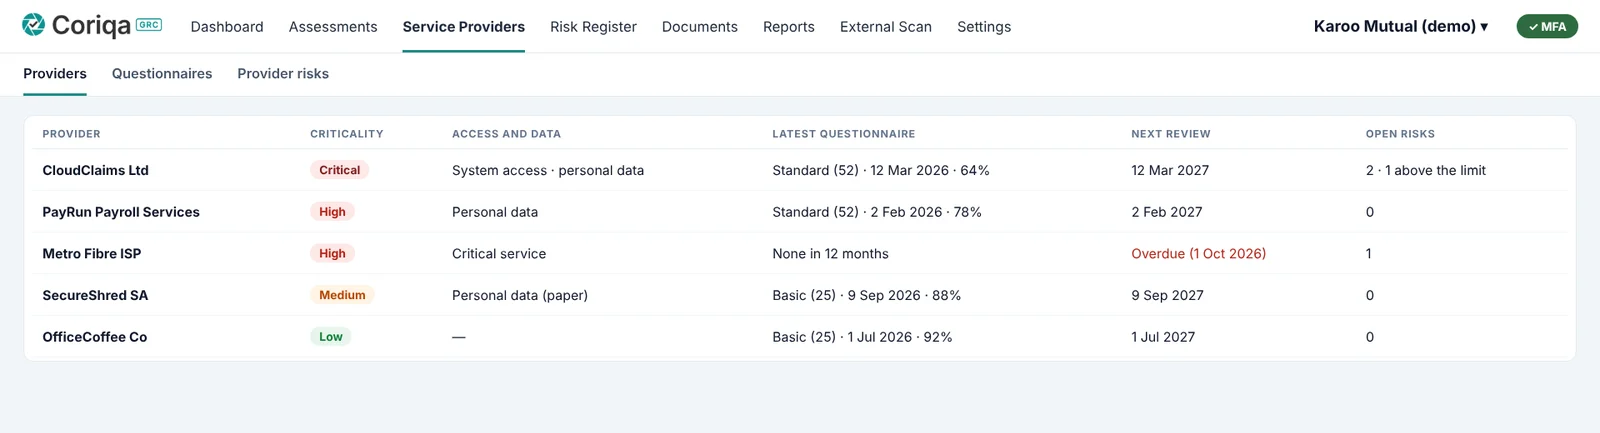
Keep every service provider with its criticality, access to your systems and data, contract and review dates. Send a questionnaire sized to how critical they are, and track provider risks in the same register.
Ten reports, as PDF or Excel
Pick a report, remove any section or part, and download. Built from the same data, so nobody spends a weekend in PowerPoint.
- Overview, board pack, risk register, score trend, remediation progress
- Policies and documents, evidence and audit pack, framework compliance
- Statement of Applicability (ISO 27001), service provider risk
Measure the technology, not just the answers
Two add-ons check what is really configured, and feed the results into the same risk register and evidence. Nothing is changed on the client's systems.
Coriqa Agent for Windows
A light, read-only agent that checks Windows 10 and 11 computers against the CIS benchmark (Level 1), with the exact CIS numbers. It runs as a Windows service and only scans when you press Scan now in Coriqa GRC.
- Failed checks become proposed risks
- Passed checks become proposed evidence
- Install with a guided setup, or the .msi for RMM, Intune or Group Policy
External scan
A passive, outside-in look at a client's domains, the way an attacker would see them: e-mail security, DNS, certificates and encryption, website security settings and privacy.
- Findings in plain words, with how to fix them
- Proposed risks for the register
- Scan monitoring repeats it on a schedule
You stay in control
Nothing goes into the register or the evidence on its own. Someone reviews each proposal in the risk register and accepts or dismisses it, and the decision is recorded.
- Accepted evidence is tagged New on the assessment
- Results kept with the assessment they prove
Audit-ready, all year round
Evidence on every answer, the gaps an auditor will question first, one set of answers for several frameworks, and an audit pack in one download.
South African regulation is in the product, not bolted on
POPIA and the Joint Standard 2 of 2024 for financial institutions sit next to the international frameworks, and the policies and playbooks are written for South African law.
One system for everyone who works on security
The CISO or vCISO runs it. Everyone else gets only the part they need.
CISO or vCISO
Sets the risk limit, plans the assessments, decides what gets fixed first and reports to the board.
In the app: Administrator, Assessment Manager
IT and control owners
Answer the questions they know, upload the evidence and work through their actions with written steps.
In the app: Editor, Risk Remediator
Risk owners
Own a risk, agree how it is treated and sign it off when the work is done.
In the app: Risk Approver
Board, exco and auditors
Get the board pack, the audit pack or the Statement of Applicability, without having to log in.
In the app: Viewer, if they want to look around
Everyone sees what they should, and nothing more
Sign-in with a second factor
Every user signs in with their own account and an authenticator app.
Roles
Administrator, Assessment Manager, Editor, Viewer, Risk Remediator, Risk Approver and Service Provider. People only see the business units they are given.
A full history
Every risk keeps its history, and deleting an assessment needs a reason that goes to the audit log.
Encrypted evidence
Evidence files are encrypted and compressed when they are stored, and only people with access to that business unit can open them.
For the people who answer for cyber security
Coriqa GRC is delivered through partners: the consultants, vCISOs and MSPs who run it with their clients and help them fix what it finds.
CISOs and security leads
One view of every business unit, a risk register the board understands, and the steps and policies to improve, without building it all yourself. Also for the IT manager who wears the security hat.
Find a partnerFinancial institutions
Assess against Joint Standard 2 of 2024 and POPIA, track the gaps to closure, and produce the evidence the regulator and the auditor ask for.
The frameworksvCISOs, consultants and MSPs
Run a virtual CISO service for all your clients from one login: a baseline assessment, a signed-off risk register and a quarterly board pack with your logo.
Partner programmeSee it in action
A 30-minute demo for partners, built around the frameworks your clients use. Looking for Coriqa GRC for your own organisation? We will introduce you to a partner.